CVE-2026-14635 is a path traversal vulnerability in the kirilkirkov Ecommerce-CodeIgniter-Bootstrap framework’s AddProduct.php controller. Small-to-mid business owners using this framework risk unauthorized file access and data breaches due to unpatched vulnerabilities.
CVE-2026-14635 Path Traversal in Kirilkirkov Ecommerce
What Happened
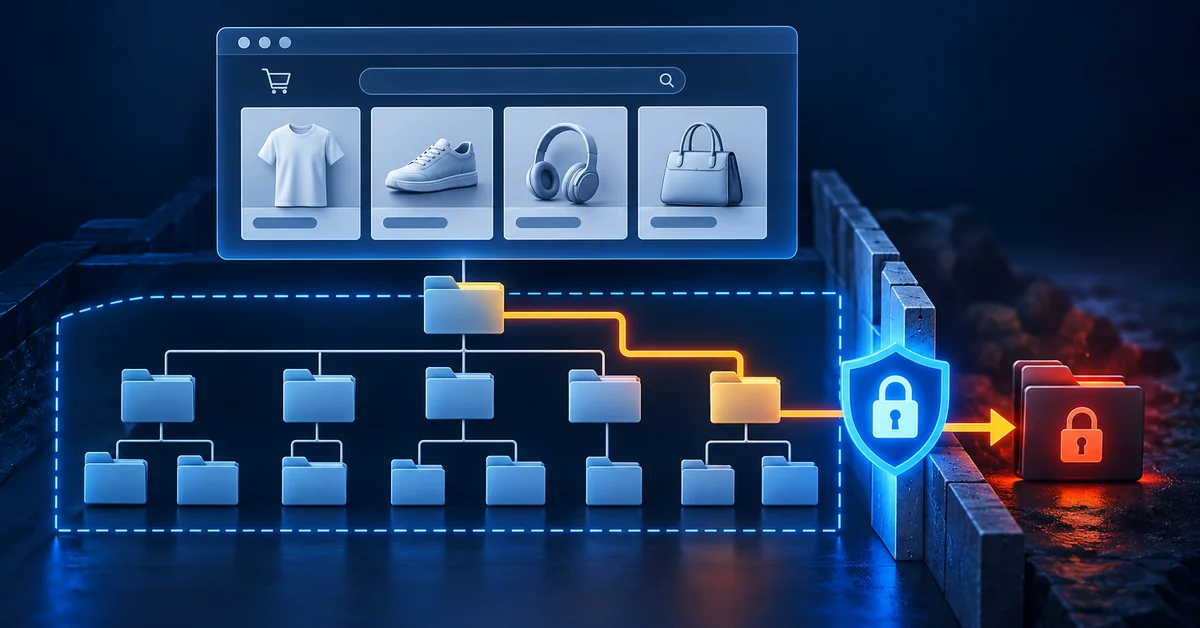
On July 4, 2026 at 16:30 UTC, the cybersecurity community discovered a new vulnerability—CVE‑2026‑14635—in the kirilkirkov Ecommerce-CodeIgniter-Bootstrap framework. The flaw surfaced within the vendor multi‑image endpoint module, specifically the `AddProduct.php` controller. Attackers can manipulate the folder argument to traverse the file system, enabling remote access to files outside the intended scope. The exploit was released publicly, allowing attackers to target any installation of this component without a patch. This event is notable because it affects an e‑commerce platform widely used by small businesses that rely on third‑party plugins for image handling.
What We Know
The vulnerability exists in version up to 222ff31c06687b1c6d0e1ab63953f82c3674c52b of the kirilkirkov package. The flaw manifests when an attacker supplies a specially crafted folder path argument, causing the application to resolve a relative path that leads outside the permitted directory hierarchy. This path traversal is possible through HTTP requests, making it remotely exploitable. No patch has been released for this version; the recommended fix is to apply the patch identified as 2a9497ff11f36e573ad99e1c357ff0e6ded49745. The CVE report notes a severity score of 0.0, indicating the vulnerability’s impact is currently unknown but could be high depending on configuration. For more technical details and updates, see the official CVE feed: News Source.
cybersecurity vendor shortlist
Why This Matters for Your Business
Small and medium‑size enterprises often rely on third‑party modules to extend their e‑commerce functionality, making them vulnerable to unpatched components. A path traversal flaw can expose sensitive business data—customer records, transaction logs, or even proprietary files stored outside the application’s public directory. If attackers gain access to such data, they could perform phishing attacks, steal customer credentials, or leak financial information, leading to regulatory fines under GDPR and PCI‑DSS compliance. In a worst‑case scenario, an attacker could manipulate inventory settings or redirect payment gateways, causing revenue loss by misdirecting transactions or triggering fraudulent charges. Moreover, reputational damage from data breaches can erode customer trust, making recovery challenging.
What You Should Do Right Now
Within the next 24 hours, immediately audit all installations of the kirilkirkov Ecommerce-CodeIgniter-Bootstrap component. Verify that you are running a version older than 222ff31c06687b1c6d0e1ab63953f82c3674c52b and check whether the patch 2a9497ff11f36e573ad99e1c357ff0e6ded49745 is available. If not, contact your vendor or consult our trusted list of vetted providers: endpoint security solutions.
During this week, implement a comprehensive security scan to identify any other path traversal vulnerabilities across your web stack. Use automated tools such as OWASP ZAP or Nessus to detect potential exploits. After 30 days, establish a patch management policy that ensures all third‑party components are regularly updated and tested for security compliance. Deploy a multi‑layer firewall and intrusion detection system to monitor suspicious file access attempts. Finally, educate your staff on safe handling of external modules and the importance of keeping software up to date.
The Bigger Picture
The emergence of CVE‑2026‑14635 underscores a growing trend of path traversal vulnerabilities in third‑party web frameworks. As e‑commerce platforms expand, they increasingly rely on plugins that may not be thoroughly vetted or updated. Attackers exploit these gaps by remotely manipulating file paths, gaining unauthorized access to critical data. This event signals the need for proactive vulnerability scanning across all external modules and a robust patch management strategy. SMBs should monitor industry trends, stay informed about new CVE releases, and prioritize securing third‑party components to mitigate potential breaches.
Key Takeaways
- Patch Immediately: Apply the latest patch for the kirilkirkov component if available.
- Audit Third‑Party Modules: Regularly check all installed plugins for known vulnerabilities.
- Deploy Security Tools: Use automated scans and intrusion detection systems to detect path traversal attacks.
- Educate Staff: Train employees on safe handling of external modules and software updates.
- Maintain Patch Management Policy: Ensure all components are kept up‑to‑date with a scheduled review cycle.
Frequently Asked Questions
Q: What is the risk if my e‑commerce platform uses this vendor?
A: If your platform incorporates the kirilkirkov module, attackers can manipulate the `AddProduct.php` path argument to traverse outside the intended directory. This could expose sensitive customer data or allow unauthorized file access. The potential impact includes data breaches, regulatory fines, and loss of revenue due to fraudulent transactions.
Q: How much does a single breach cost?
A: A compromised e‑commerce platform can incur up to $15 000 in lost revenue, plus additional costs for remediation, legal compliance, and reputational damage. The exact figure depends on the volume of transactions affected and the extent of data exposure.
Q: What steps can I take that my non‑technical team can perform?
A: Conduct a basic security audit by reviewing your software versions and verifying patch availability. Use free tools like OWASP ZAP or Nessus for scanning vulnerabilities. If you need deeper expertise, consult our vendor shortlist to secure the component.
Q: Who is most likely targeted in this scenario?
A: Small‑to‑mid‑size e‑commerce businesses that rely on third‑party modules without rigorous security checks are the primary target. These companies often lack dedicated IT teams and thus may be overlooked by attackers seeking exploitable vulnerabilities.
How DefendMyBusiness Can Help
DefendMyBusiness offers a network of 400+ vetted technology providers, ensuring your business is matched with reliable vendors for this specific threat category. We recommend engaging our free-security-scan service to identify any path traversal vulnerabilities in your system. Additionally, we can connect you with trusted endpoint security experts who can implement the patch and establish ongoing monitoring. For further assistance, contact us at https://defendmybusiness.com/contact.
Sources
Tags: security, e-commerce, path traversal, small-business cybersecurity
Recommended Endpoint Security Vendors
DefendMyBusiness partners with a curated network of 400+ vetted providers. Here are 4 currently active in our channel ecosystem for endpoint security:
| Vendor | Specialty |
|---|---|
| Lunavi | As a leading managed service provider and consulting firm, Lunavi helps customers advance their digital transformation goals by building mod |
| XTIUM | At XTIUM, we do more than support your Clients’ IT – we integrate, secure, and optimize it. Our mission is simple: We make your clients’ IT |
| Unisys | Unisys is a global technology solutions company that powers breakthroughs for the world’s leading organizations. Our solutions & digital wor |
| ECI | |
Get a free tailored shortlist – we match you with 3 of these vendors based on your size, industry, and priorities. 24-hour turnaround, no obligation.
Run a Free Security Scan
See exactly where your business is exposed to threats like the one in this article. Plain-English report, no credit card, no sales calls.