Cybersecurity threats are constantly evolving. Hackers are developing new methods for breaking into networks, stealing information, and interfering with business processes. Bad actors frequently achieve their objectives by exploiting weaknesses, and their velocity is increasing.
According to the FBI IC3 report, the FBI’s Internet Crime Complaint Center logged 1,008,597 complaints and $20.877 billion in claimed cybercrime losses in 2025.
One of the best strategies for avoiding cybersecurity threats is routine pentesting or network penetration testing. Penetration testing replicates a real-world attack on your systems, allowing you to detect potential flaws and vulnerabilities. It is broadly classified into internal and external pentesting.
This guide explains the difference between these two types of tests and when you should apply them. Let’s get started.
Internal vs External Pen Testing: Key Differences
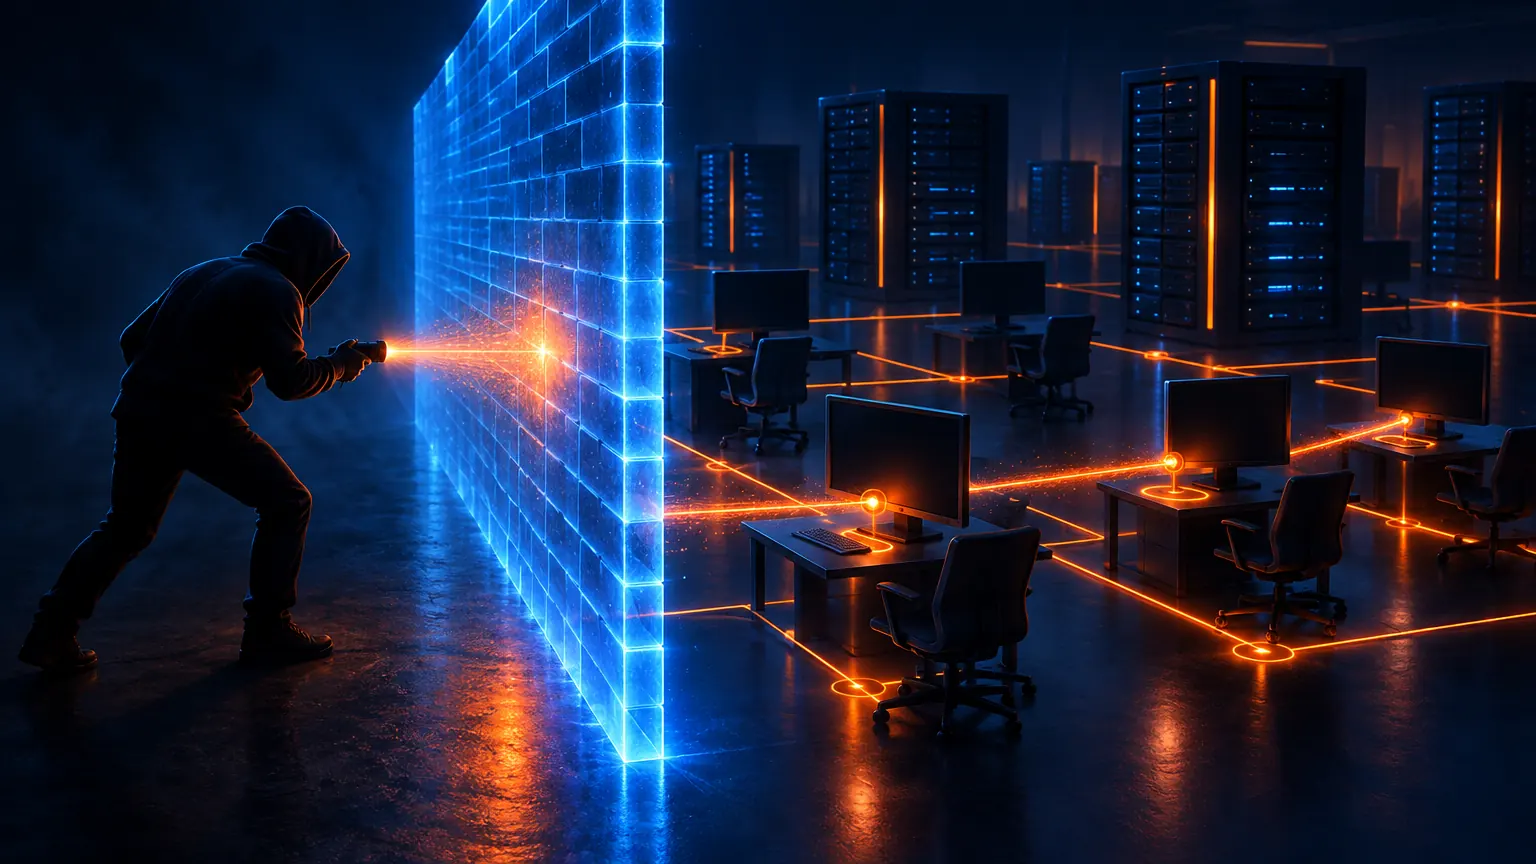
External penetration testing assesses how your internet-facing systems could be compromised by an external attacker. It mimics an attacker who has zero access and solely probes your websites, VPNs, firewalls, email servers, and other perimeter assets.
Internal penetration testing, also known as an internal network assessment, finds weaknesses in internal systems, software, and user privileges by simulating an attack from within your company’s network. This test simulates the access a threat actor obtains after getting past your external defenses or the permissions an employee may have.
The two answer distinct queries; thus, most mature security programs run both. Your compliance requirements and your riskiest situation will determine which one comes first.
Detailed Comparison: Internal vs External Pen Testing
Both tests employ similar methodologies, but they differ in where the tester begins and what the results reveal. Access, scope, threats, compliance, cost, and timing are the six factors that buyers consider most important when comparing the two strategies.
Attacker Starting Position
An external pen test, like an anonymous online attacker, begins with no access. The tester only has access to information obtained from public sources. An internal test begins within the network, usually with a device connected to an office port or a regular user account. This scenario represents an attacker who has already established a presence.
Assets and Scope
External network penetration testing covers all public-facing assets, including websites, VPN gateways, mail servers, DNS, and your firewall. Internal testing includes workstations, servers, shared files, databases, and Active Directory behind the network’s perimeter. Because the two scopes are different, one test cannot replace the other.
Cost and typical duration
The cost of the test is determined by its extent rather than its label. Prices often scale based on the number of IP addresses, hosts, apps, and locations, as well as test depth and reporting. There is no set time limit for either test. A large internal network takes longer to complete than a small outward footprint. Thus, before comparing pricing, you should request scoped quotes.
Threats each simulate
External tests can mimic social engineering directed at employees, OSINT-driven targeting, and opportunistic scanning. On the other hand, internal testing mimics a hacked laptop, an insider threat, or malware that has already gotten past your defenses. So, every model corresponds to a distinct phase of an actual attack.
Compliance and audit fit
Internal and external penetration testing is mandated by PCI DSS v4.0.1 at least once every 12 months, as well as following any major changes to infrastructure or applications. A pen test is not required by SOC 2. However, criterion CC4.1 identifies penetration testing as one type of evaluation that management can utilize, and auditors frequently request the results.
When to run it
After launching or making major changes to internet-facing systems, conduct external tests. Internal checks are necessary following significant network modifications, mergers, or security events. After remediation, retest both to make sure the fixes are effective. Additionally, if you are eligible for PCI DSS, schedule both at least once a year.
Where Each Option Wins in Internal vs External Pen Testing
Neither test is superior in every scenario. The best option depends on the risk you need to assess because each one identifies a distinct kind of weakness. Below are the advantages of each external and internal penetration test:
External penetration testing strengths
1. Tests internet-facing exposure
External testing identifies what the internet can see and exploit. It locates forgotten hosts, out-of-date software, vulnerable setups, and exposed services. After that, you can reduce your attack surface before actual attackers discover the same vulnerabilities. This is especially important for companies that use remote access, APIs, or customer portals.
2. Validates perimeter defenses
This test determines whether your firewall and network perimeter rules block actual attack methods. You therefore discover which defenses are effective and which are only theoretical. Additionally, you obtain data to inform patch priority and rule modifications.
3. Mirrors an outside attacker
To identify employee names, exposed subdomains, and leaked information, testers first collect OSINT, much like an outsider would. The amount of information you disclose is then determined by a black box vs. white box option, ranging from all network specifics to none at all. More information means deeper coverage per testing day; less information is more realistic.
Internal penetration testing strengths
Now, let’s discuss the strengths of internal penetration testing.
Models insider and breach risk
Internal testing addresses both the insider threat and the expected breach scenarios. It illustrates the potential harm caused by a contractor, a malicious employee, or an attacker using a stolen account. An assumed breach begins with intentional access, so time is spent on impact rather than getting in.
Finds lateral-movement paths
Testers employ weak credentials, repeated passwords, and incorrect setups to switch between hosts. This highlights opportunities for privilege escalation and lateral movement routes that automated scans frequently overlook. The outcome demonstrates how a single compromised device could escalate into a larger problem.
Checks segmentation and Active Directory
Internal testing confirms that internal network segmentation does isolate critical systems. Additionally, they check Active Directory for attack routes leading to domain administrator access, excessive permissions, and weak passwords. These checks are important because flat networks and overprivileged accounts allow attackers to move swiftly once inside.
Internal vs External Pen Testing: Which One is Suitable for Your Business
Your ideal starting point depends on what has changed, what you need to prove, and which risks concern you most. These four typical scenarios show how companies typically align a test with a demand.
New public-facing apps
Introducing an API or customer portal? External testing should come first. It verifies input handling, exposure, and authentication before attackers discover weaknesses. Web applications may additionally require a specific application-layer test, as network tests do not cover all application flaws. Retest after every major release.
Post-breach assurance
Conduct internal testing following an incident to see if comparable attack routes are still accessible. Assumed breach exercises demonstrate the robustness of segmentation, detection, and credential resets once an individual has gained access. Assign each discovery an owner and a retest date by pairing them with remedial tracking.
PCI or SOC 2 scope
According to PCI DSS regulations, both test types must be performed at least once every 12 months and following major changes. SOC 2 does not require them, but the data can help you improve your monitoring and vulnerability management systems. Document the scope so that assessors may link each tested system to the audited environment.
Full-spectrum annual testing
Every year, security teams seeking wide assurance include both tests, along with retests following significant modifications. When combined, they cover both inside-out and outside-in routes, providing executives with a more comprehensive risk picture. Additionally, you may prioritize remediation based on actual attack vectors rather than just raw vulnerability counts thanks to integrated findings.
What is the difference between internal and external penetration testing?
External penetration testing examines internet-facing systems from the perspective of an outsider and illustrates potential points of entry. Internal penetration testing begins within your network and mimics an insider or a compromised device to demonstrate the extent of an attacker’s capabilities. The results vary depending on the scope, initial access, and threat model.
Do I need both internal and external pen testing?
Yes, most of the time. Different questions are addressed by the two tests. Internal tests measure the effects once someone has access, and external tests evaluate exposure from the internet. Both are necessary for in-scope environments under PCI DSS. Outside of PCI, a risk-based program frequently incorporates both, as a robust perimeter does not prevent a stolen password or an insider.
Which penetration test should I run first?
If you have exposed assets and no recent baseline, start with external testing, as it can shut the easiest entrance holes. However, start with internal testing if you are most concerned about an insider threat or a previous breach. Plan both within the same 12-month period if PCI DSS is applicable.
How often should each test be performed?
Test after major modifications and at least once a year. For in-scope entities, that cadence corresponds with PCI DSS timing. Testing may be more frequent in high-risk or dynamic contexts. After remediation, retest to make sure the fixes are effective.
Does PCI DSS require internal and external testing?
Yes. PCI DSS v4.0.1 Requirements 11.4.2 and 11.4.3 call for internal and external penetration testing at least once every 12 months and after significant changes. Segmentation testing falls under separate requirements. Review the PCI SSC library for the full text.
How much does each penetration test cost?
Prices differ greatly. The majority of the cost is determined by scope, which includes test depth, reports, IP addresses, apps, and locations. Therefore, rather than depending on flat pricing lists, ask delivery partners for scoped prices.
Want help getting your security solution right?
Defend My Business helps SMBs cut through the marketing and get their security solution right for their environment, budget, and compliance needs — then deploy and manage it. Through our 400+ vendor network we can often secure better pricing and terms than buying direct, and we stay vendor-neutral, so the recommendation fits you, not a sales quota. Want a second opinion? Pair this with our cybersecurity consulting or talk it through with an advisor.
Book a free call with a DMB advisor →