The U.S. DHS is investigating a cyber breach at an information-sharing network that flagged anomalous traffic and unauthorized access. Small-to-mid business owners should review their own cybersecurity protocols to prevent similar breaches and ensure data protection.
US DHS Investigates Cyber Breach at Information‑Sharing Network
What Happened
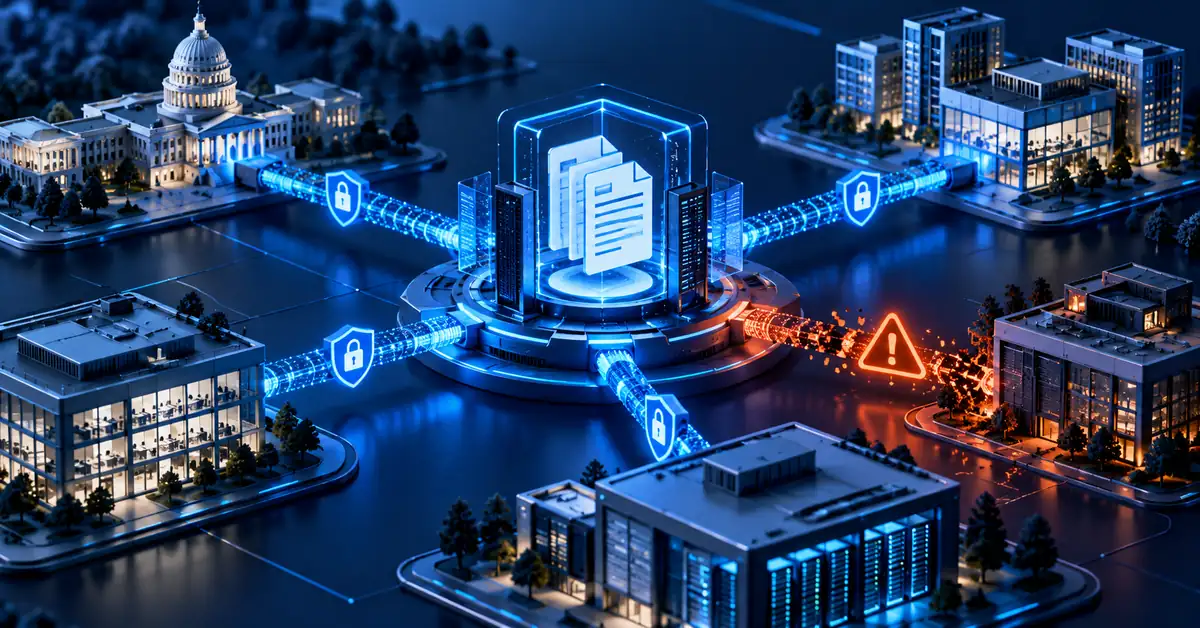
The U.S. Department of Homeland Security (DHS) announced that it is probing a cyber breach affecting an information‑sharing network, as reported by Reuters on 2026‑07‑02. The incident was identified shortly after the network’s internal audit flagged anomalous traffic patterns and unauthorized access attempts. DHS officials stated that investigations are underway to ascertain the source of the intrusion and potential data compromise. This event highlights a significant breach in a critical infrastructure that facilitates inter‑agency communication, raising concerns about national security and operational continuity.
What We Know
The breach involves a network used for sharing sensitive information among federal agencies. According to Reuters, the DHS investigation began on 2026‑07‑02, following an internal audit that revealed unusual traffic and unauthorized access attempts. While specific details of the attack vector are not disclosed publicly, it is likely to involve compromised credentials or malware infiltration. The incident underscores the vulnerability of shared networks where multiple entities rely on a common platform. For context, recent analyses by the National Cybersecurity Advisory (NCA) indicate that similar breaches have occurred in other federal networks, emphasizing the need for robust authentication and monitoring protocols. cybersecurity vendor shortlist
Why This Matters for Your Business
Businesses that depend on shared communication platforms—especially those collaborating with governmental agencies or partners requiring secure data exchange—are at heightened risk. A breach could expose sensitive client information, lead to regulatory fines under the GDPR or HIPAA, and disrupt operational workflows. Small and mid‑size firms often lack dedicated security teams, making them more vulnerable to such attacks. This event signals that even well‑protected networks can be compromised, potentially affecting your business’s reputation and financial stability. managed cybersecurity services
What You Should Do Right Now
Immediate actions within 24 hours: 1) Conduct a thorough audit of all shared network connections and access logs to identify unauthorized activity; 2) Verify and enforce multi‑factor authentication for all users accessing the platform; 3) Temporarily isolate affected systems from external networks while investigation continues. Within this week, plan to deploy endpoint security solutions such as antivirus and intrusion detection systems across all devices. Over the next 30 days, establish a comprehensive incident response plan that includes regular vulnerability assessments, patch management, and staff training on secure practices. Even without a technical team, you can initiate a free security scan by contacting our network of vetted vendors. endpoint security solutions
The Bigger Picture
This breach reflects a broader trend in the threat landscape where shared infrastructures become prime targets for attackers exploiting credential theft or malware. Recent reports from the CISA highlight that such attacks are increasingly common across government and enterprise networks, underscoring the necessity of heightened security posture. Businesses should monitor for signs of unauthorized access patterns, unexpected traffic spikes, and anomalous login attempts, as early detection can mitigate potential damage.
Key Takeaways
- Conduct immediate audit of shared network logs to detect anomalies.
- Enforce multi‑factor authentication for all users accessing sensitive platforms.
- Deploy endpoint security solutions to protect devices across the organization.
- Initiate a free security scan using our vetted vendor network.
Frequently Asked Questions
Q: How can my small business mitigate risks from shared government networks?
A: Small businesses should adopt stringent access controls, ensuring only authorized personnel can connect to shared platforms. Implementing multi‑factor authentication and monitoring logs for suspicious activity will help prevent unauthorized breaches. Additionally, regular security audits and staff training on secure practices are essential.
Q: What is the cost of implementing endpoint security solutions?
However, many vendors offer tiered pricing or discounts for bulk purchases.
Q: What next steps should I take after detecting unauthorized access?
A: Immediately isolate affected systems from external networks, conduct a detailed investigation to identify the source, and apply patches or reconfigure authentication settings. Following that, establish an incident response plan with defined roles, communication protocols, and escalation procedures.
Q: Which industries are most vulnerable to shared network breaches?
A: Industries such as healthcare, finance, logistics, and public sector organizations rely heavily on shared data exchanges, making them prime targets for cyber attacks. Small businesses in these sectors should prioritize robust security measures to protect sensitive information.
How DefendMyBusiness Can Help
DefendMyBusiness offers a 400+ technology provider network that matches businesses to pre‑vetted vendors specializing in endpoint security and network monitoring solutions. By leveraging our vetted vendor list, you can quickly deploy the most relevant services for this incident type. Initiate a free security scan with security scan or contact us at https://defendmybusiness.com/contact for tailored advice.
Sources
News Source
NCSA Cyber Threat Analysis
Tags: security, cybersecurity, business risk, DefendMyBusiness
Recommended Endpoint Security Vendors
DefendMyBusiness partners with a curated network of 400+ vetted providers. Here are 4 currently active in our channel ecosystem for endpoint security:
| Vendor | Specialty |
|---|---|
| XTIUM | At XTIUM, we do more than support your Clients’ IT – we integrate, secure, and optimize it. Our mission is simple: We make your clients’ IT |
| ECI | |
| Ntegrated | At Ntegrated we believe every company deserves to have the best possible work experience, regardless of what they do and where they do it. A |
| Powernet | Powernet is a Woman-Owned business with more than 30 years of experience and expert sales, engineering, and support teams, which provide our |
Get a free tailored shortlist – we match you with 3 of these vendors based on your size, industry, and priorities. 24-hour turnaround, no obligation.
Run a Free Security Scan
See exactly where your business is exposed to threats like the one in this article. Plain-English report, no credit card, no sales calls.