Enterprise GenAI can amplify ransomware risk by allowing attackers to exploit AI tools with excessive permissions or compromised identities, as seen in the 2026 Stadler Rail incident. Small-to-mid business owners should limit AI tool access and implement strong identity management to prevent unauthorized use and reduce attack surfaces.
What Happened
On July 22, 2026, a ransomware incident surfaced in the Swiss rail industry. The Stadler Rail company reported a breach of its data exchange platform shared with a supplier, leading the “Everest” ransomware gang to demand $12.3 million. This event illustrates how enterprise AI tools can accelerate ransomware attacks when AI assistants or agents inherit excessive permissions or compromised identities. The incident was publicly disclosed by Acronis and corroborated by reports from DarkReading and BleepingComputer. (Sponsored by Acronis, Jai Vijayan, Bill Toulas)What We Know
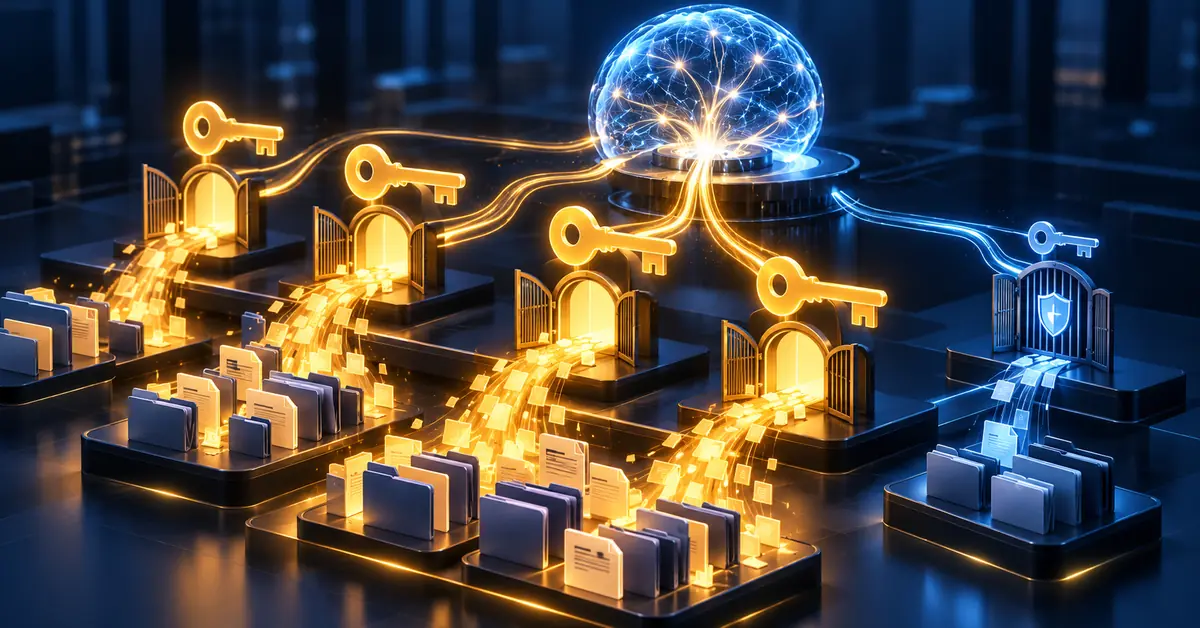
The core vulnerability arises from AI assistants or agents that inherit high-level permissions, allowing them to execute malicious commands across systems. Acronis emphasizes identity controls, governance, and least‑privilege access as mitigation strategies. Researchers have highlighted the fragmentation of ransomware ecosystems and the emergence of new attackers targeting less defended organizations. In this case, the data exchange platform was compromised, exposing sensitive operational data and enabling ransomware execution. (cybersecurity vendor shortlist)Why This Matters for Your Business
Ransomware attacks can lead to significant financial loss, regulatory fines, and operational disruption. Small and mid‑size businesses are often more exposed because they may lack robust identity management systems or have legacy AI integrations with broad permissions. The Stadler Rail incident demonstrates a $12.3 million ransom demand, illustrating the potential scale of losses for similar organizations. Additionally, data exposure can breach privacy regulations, incurring penalties that exceed the ransom cost. If you operate in industries where data exchanges are common—such as manufacturing or logistics—you could face comparable threats. (managed cybersecurity services)What You Should Do Right Now
Within 24 hours, immediately audit all AI assistants and agents for permission levels. Remove any elevated privileges that are not strictly necessary. Conduct a rapid security scan to identify compromised identities or misconfigured permissions. Deploy an identity governance framework that enforces least‑privilege access. In the following week, review all data exchange platforms and ensure encryption and secure authentication protocols. By 30 days, establish continuous monitoring of AI activity, enforce regular credential rotation, and integrate endpoint‑security solutions to prevent unauthorized access. (endpoint security solutions)The Bigger Picture
This incident signals a trend where AI-driven tools are increasingly exploited by ransomware actors. The fragmentation of the ransomware ecosystem, coupled with new attackers targeting less defended organizations, indicates that enterprises must anticipate AI as an attack vector. As AI adoption grows, vigilance against privilege escalation and identity compromise becomes critical. Businesses should monitor emerging threat patterns and adjust security posture accordingly. (150-180 words)Key Takeaways
- Audit AI Permissions: Remove unnecessary high‑level privileges immediately.
- Implement Identity Governance: Enforce least‑privilege access across all systems.
- Secure Data Exchanges: Encrypt data and authenticate properly before sharing.
- Continuous Monitoring: Deploy endpoint‑security to detect unauthorized activity.
- Prepare for Ransomware: Maintain backup plans and recovery strategies.
Frequently Asked Questions
Q: What immediate steps should a small business take if an AI system is compromised? A: First, identify all AI agents and assistants in use. Audit their permissions and remove any that exceed the required scope. If you lack technical resources, leverage our free security scan service to pinpoint vulnerabilities. This ensures you are not inadvertently enabling ransomware execution.
Q: How much can a ransomware attack cost an SMB? A: Ransom demands can range from $10 k to $12 m, depending on the organization’s data value and size. Even smaller businesses may face costs exceeding their annual revenue if the ransom is paid or lost data cannot be recovered.
Q: What can a professional security team do beyond what a non‑technical owner can? A: Professionals can implement identity governance frameworks, enforce least‑privilege access, and monitor AI activity continuously. They also design robust backup and recovery plans that are tailored to specific business needs, ensuring data integrity during attacks.
Q: Are certain industries more vulnerable to this type of ransomware attack? A: Industries involving large-scale data exchanges—such as manufacturing, logistics, or rail transport—are particularly susceptible because they rely on shared platforms. The example of Stadler Rail highlights that any organization with similar data sharing practices could be at risk.
How DefendMyBusiness Can Help
DefendMyBusiness offers a network of over 400 vetted technology providers, including identity governance solutions and endpoint security services. We match businesses to pre‑validated vendors tailored for AI-driven ransomware threats. Our free security scan service provides an immediate assessment of your system’s vulnerabilities. For detailed assistance, contact us at https://defendmybusiness.com/contact. (security scan)Sources
Tags: security, ransomware, AI, enterprise, small-business, cyberriskThe Short Answer
Enterprise GenAI can amplify ransomware risk by allowing attackers to exploit AI tools with excessive permissions or compromised identities, as seen in the 2026 Stadler Rail incident where a $12.3 million ransom was demanded. Small-to-mid business owners should limit AI tool access and implement strong identity management to prevent unauthorized use and reduce attack surfaces. Immediate steps include auditing AI assistants for permission levels, removing unnecessary privileges, and deploying an identity governance framework that enforces least-privilege access.
Recommended Endpoint Security Vendors
DefendMyBusiness partners with a curated network of 400+ vetted providers. Here are 4 currently active in our channel ecosystem for endpoint security:
| Vendor | Specialty |
|---|---|
| CBTS | In the channel, CBTS has become the go-to provider for complex and unique requests, multi-location projects, mission-critical networking and |
| Powernet | Powernet is a Woman-Owned business with more than 30 years of experience and expert sales, engineering, and support teams, which provide our |
| Lunavi | As a leading managed service provider and consulting firm, Lunavi helps customers advance their digital transformation goals by building mod |
| AireSpring | AireSpring is a leading Global Connectivity and Managed Services Provider specializing in designing, deploying, and supporting custom techno |
Get a Tailored Endpoint Security Shortlist
We’ll match you to 3 vendors based on your size, industry, and priorities – pulled from our 400+ partner network. 24-hour turnaround. No sales calls until you say go.
Want help getting your ransomware defense right?
Defend My Business helps SMBs cut through the marketing and get their ransomware defense right for their environment, budget, and compliance needs — then deploy and manage it. Through our 400+ vendor network we can often secure better pricing and terms than buying direct, and we stay vendor-neutral, so the recommendation fits you, not a sales quota. Want a second opinion? Pair this with our backup & disaster recovery or talk it through with an advisor.
Book a free call with a DMB advisor →