HollowGraph is a new malware that uses Microsoft Graph’s calendar feature for stealthy command-and-control communications. Small-to-mid business owners should monitor their Microsoft 365 accounts for suspicious calendar invites and ensure all systems are up to date to mitigate risks.
What Happened
On 2026‑07‑20, a new malware strain dubbed HollowGraph was disclosed by cybersecurity experts. The threat exploits the calendar feature within compromised Microsoft 365 mailboxes as a covert command‑and‑control (C2) channel. Attackers inject malicious commands disguised as ordinary calendar invites, allowing the malware to receive instructions and exfiltrate stolen data without triggering alerts. Reports were first published on BleepingComputer and later corroborated by other security news outlets. The attack surfaced during a period when Microsoft announced that OneDrive sync app updates would cease for Windows 10 version 21H2 and earlier, creating additional support concerns for legacy systems.What We Know
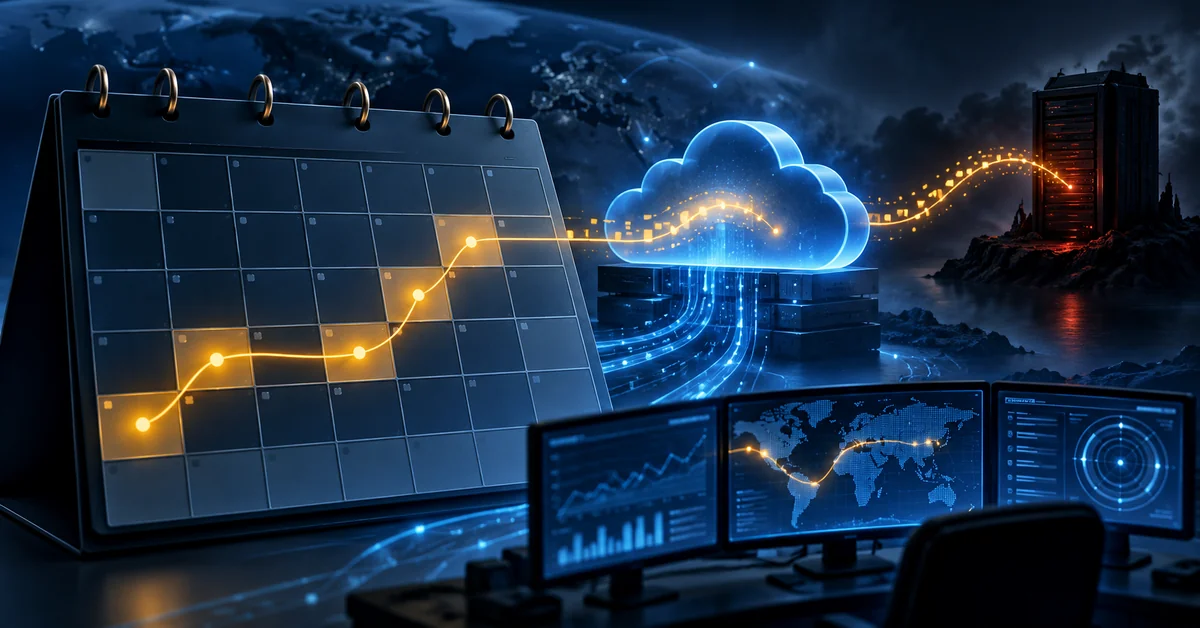
The HollowGraph malware is a .NET‑compiled component that abuses the Microsoft Graph API via a compromised Microsoft 365 account. It transforms the mailbox’s calendar into a covert two‑way “dead drop” for hackers. Attackers can embed commands within calendar invites, which are normally processed by Office 365 clients without suspicion. The malware leverages the API to retrieve and exfiltrate sensitive data from victim accounts, including emails, attachments, and user credentials. This approach is unique because it uses a legitimate feature that most users trust, thereby bypassing traditional intrusion detection systems. One source reports that this technique has been observed in multiple corporate environments, highlighting its potential for widespread exploitation. cybersecurity vendor shortlistWhy This Matters for Your Business
Small and mid‑size businesses are particularly vulnerable because they often rely on Microsoft 365 services without robust security controls. The HollowGraph attack can compromise confidential information—such as client records, financial data, or intellectual property—without triggering alerts. Potential consequences include revenue loss due to compromised transactions, regulatory fines if sensitive data is exposed (e.g., GDPR violations), and operational disruptions from system downtime. Businesses that run legacy Windows 10 endpoints may also face additional complications due to Microsoft’s discontinuation of OneDrive updates, further amplifying risk.What You Should Do Right Now
Within 24 hours, perform an immediate audit of all Microsoft 365 accounts for unusual calendar invites and verify the integrity of the Microsoft Graph API. Disable or restrict access to the calendar feature in critical accounts until a review is complete. Conduct a free security scan on your endpoints to detect any hidden malware components—this can be done using our internal tools or community‑approved scanners. If you lack an IT team, consider contacting DefendMyBusiness for vendor recommendations that specialize in endpoint and network security. Within the next week, implement strict mailbox access controls, enforce multi‑factor authentication for all Microsoft 365 users, and deploy a centralized monitoring system to flag suspicious calendar activity. Over the following 30 days, develop a comprehensive incident response plan, including data backup and recovery protocols, and schedule regular vulnerability assessments.The Bigger Picture
The HollowGraph attack illustrates a growing trend where attackers repurpose legitimate cloud services for stealthy communication channels. Microsoft 365 is widely adopted by SMBs and enterprises alike, making it an attractive target. Similar incidents—such as the use of calendar invites for malware commands—have emerged across various sectors, indicating that defenders must adopt proactive monitoring of all seemingly benign features. Future threats may involve leveraging other Office 365 APIs or third‑party integrations to hide malicious activity. Businesses should keep abreast of Microsoft’s security updates and ensure their systems remain compliant with the latest support guidelines.Key Takeaways
- Audit your calendars immediately: Scan for suspicious invites and verify API integrity.
- Disable calendar access temporarily: Restrict usage in critical accounts until a review is complete.
- Employ multi‑factor authentication: Strengthen user security across Microsoft 365.
- Deploy a monitoring system: Flag any unusual calendar activity to detect hidden malware.
- Plan incident response: Prepare backup and recovery procedures to mitigate damage.
Frequently Asked Questions
Q: How can I identify if my Microsoft 365 mailbox has been compromised by HollowGraph? A: Look for unexpected calendar invites that contain non‑standard URLs or attachments. If an invite appears in a user’s calendar but the sender is unknown, investigate further. Verify that the invite does not trigger any alerts from your security monitoring tools. The presence of malicious payloads can often be detected by scanning the attached files for known malware signatures.
Q: What is the cost to mitigate this threat if I lack an IT team? A: Using a free security scan tool can identify hidden components with minimal effort and no additional cost. This investment can prevent costly data breaches and regulatory penalties.
Q: What preventive measures should I implement to avoid future attacks using similar tactics? A: Enforce strict mailbox access controls, disable calendar features for non‑critical users, enforce MFA, and deploy centralized monitoring of all Microsoft 365 APIs. Professional security consultants can provide advanced threat detection and incident response plans that are beyond the capabilities of a non‑technical team.
Q: Which industries are most at risk from this type of attack? A: Industries heavily reliant on Microsoft 365 for client communication—such as law firms, healthcare providers, and finance services—are most susceptible. These sectors often handle sensitive data that could be compromised by malicious calendar-based communications.
How DefendMyBusiness Can Help
DefendMyBusiness offers a network of over 400 vetted technology providers tailored to your specific threat landscape. We match SMBs with specialized vendors for endpoint security, network protection, and advanced monitoring solutions. Our free-security-scan service can quickly identify hidden malware like HollowGraph on your systems. For more robust defense, we recommend consulting our vendor shortlist and contacting us at https://defendmybusiness.com/contact.Sources
Tags: security, cybersecurity, business risk, DefendMyBusiness, Microsoft 365, SMB protectionThe Short Answer
Small-to-mid business owners should audit their Microsoft 365 accounts within 24 hours for suspicious calendar invites and disable calendar access in critical accounts temporarily to mitigate HollowGraph risks. The malware uses Microsoft Graph’s calendar feature as a covert C2 channel, embedding malicious commands in invites that bypass traditional detection systems. Immediate action is crucial due to the potential for data exfiltration and operational disruption. Ensure all systems are up to date, especially legacy Windows 10 endpoints affected by discontinued OneDrive updates.
Recommended Endpoint Security Vendors
DefendMyBusiness partners with a curated network of 400+ vetted providers. Here are 4 currently active in our channel ecosystem for endpoint security:
| Vendor | Specialty |
|---|---|
| CBTS | In the channel, CBTS has become the go-to provider for complex and unique requests, multi-location projects, mission-critical networking and |
| ECI | |
| Powernet | Powernet is a Woman-Owned business with more than 30 years of experience and expert sales, engineering, and support teams, which provide our |
| Unisys | Unisys is a global technology solutions company that powers breakthroughs for the world’s leading organizations. Our solutions & digital wor |
Run a Free Security Scan
See exactly where your business is exposed to threats like the one in this article. Plain-English report, no credit card, no sales calls.
Want help getting your security solution right?
Defend My Business helps SMBs cut through the marketing and get their security solution right for their environment, budget, and compliance needs — then deploy and manage it. Through our 400+ vendor network we can often secure better pricing and terms than buying direct, and we stay vendor-neutral, so the recommendation fits you, not a sales quota. Want a second opinion? Pair this with our cybersecurity consulting or talk it through with an advisor.
Book a free call with a DMB advisor →